HITRUST CSF certification
HITRUST CSF has become a widely adopted security and privacy framework. It creates a defined and holistic set of requirements to assess business applications and systems related to the secure storage and transmission of electronic data. Adoption has rapidly become a standard requirement across the healthcare industry, as many insurance payers, hospitals and health systems require vendors to achieve certification as part of their third-party risk management efforts.
HITRUST incorporates multiple security and privacy standards as well as regulatory requirements, under one holistic program. The various intersections between these information technology frameworks and health care regulations make implementing the program complex, especially for organizations without adequate dedicated resources for the effort.
The benefits of certification
- Increases your ability to secure high-value contractual relationships with major health care providers, insurance payors and more
- Establishes credibility and trust in the effectiveness of your privacy and security controls
- Provides assurances of risk management and compliance to dozens of regulatory bodies
- Helps to address evolving cyberthreats with access to continuously updated methodologies and solutions
- Creates more efficient processes in responding to request-for-proposal questionnaires and eliminates the need for multiple assessments and single-use reports
- Reduces your risk exposures and can lead to more favorable cyber insurance premiums
Certification types: e1, i1 or r2
There are three different HITRUST certification options: e1, i1 and r2. Knowing which assessment is right for your organization requires an understanding of your budget, resources and risk.
Cyber essentials 1-year (e1)
Certification addresses essential cybersecurity hygiene utilizing 44 static control requirements. This one-year certification takes about half the effort to implement as the i1 certification and provides basic-level assurances.
Implemented 1-year (i1)
Provides your organization with cybersecurity leading practices utilizing 182 static control requirements. This one-year certification requires moderate effort to implement and provides moderate cybersecurity assurances.
Risk-based 2-year (r2)
Provides your organization with an expanded approach to risk management and compliance evaluation. This complex, two-year certification is tailored to your organization and utilizes a library of 2000+ control requirements. On average, an r2 certification uses 450 tailored control requirements and takes a significantly higher lever of effort to implement.
Guiding you through the HITRUST CSF journey
While HITRUST CSF is a standardized framework to address certification, it’s meant to be used as a guide. Additional considerations must be weighed for each organization.
To help organizations with certification, RSM works to create a customized road map that is designed to address the organization’s structure, goals, culture and systems. That road map not only helps you achieve HITRUST CSF certification but also helps you continually upgrade and enhance your program to meet the ever-changing risk and regulatory landscape.
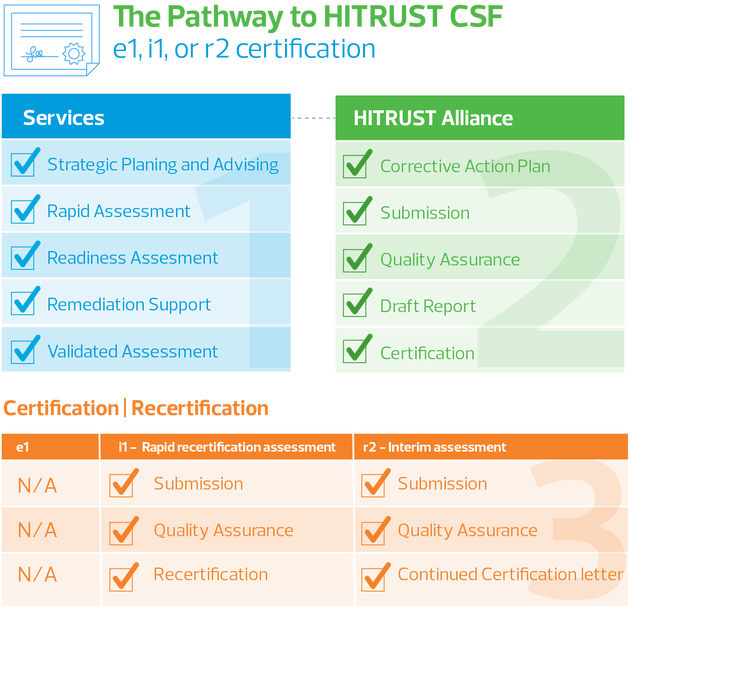
The pathway to certification
A HITRUST CSF-validated assessment is the final phase required prior to submitting for certification consideration to the HITRUST Alliance. As an authorized external assessor firm, RSM will conduct the HITRUST CSF-validated assessment in accordance with the HITRUST Alliance’s assurance program requirements. If eligible, RSM will manage the HITRUST Alliances quality assurance process to help your organization achieve HITRUST CSF certification.
If your organization qualifies, RSM can also leverage your HITRUST r2 validated assessment to provide additional certifications, including NIST CSF and (SOC) 2.
Integral partner to your HITRUST CSF journey
When you need outside assistance, it is important to choose the right advisor.
RSM understands the issues you face and will work with you to tailor a HITRUST CSF implementation plan that fits your organization's structure and culture. Our process has helped clients of all sizes create confidence in their security and privacy program.
See what others are saying:
I would picture [RSM] as not a vendor, but as a partner that has really helped us not only improve our security but also benefit our business.
Chief Information Security Officer, Cecelia Health
RSM brings the right people with the right skills to the table every time. The RSM people I’ve interacted with all act with integrity and are responsive to feedback.
System Vice President and Chief Information Security Officer, SSM Health
RSM’s breadth, depth, knowledge and commitment to their customers has led to a longstanding partnership that has enabled us to successfully mature and grow our risk management program.
Vice President, Chief Information Security Officer, a Top US Health System