Cyber risk assessment services
What is a cyber risk assessment?
A cyber risk assessment is a process used to identify, evaluate, and prioritize potential threats and vulnerabilities to an organization's information systems and data. Its purpose is to determine where security gaps may exist and to develop and implement strategies to reduce these risks, aiming to safeguard the organization from financial loss, operational disruption, or reputational impact resulting from cyberattacks.
Conducting a cyber risk assessment is important because it:
- Enhances security posture by identifying and addressing vulnerabilities before exploitation occurs.
- Assists organizations in allocating resources to address the most significant risks and critical assets, which can improve the effectiveness of security investments.
- Provides data for executives and stakeholders to make decisions regarding security investments and risk tolerance.
- Contributes information to the development of incident response and recovery plans by highlighting potential points of failure.
- Supports compliance with regulatory requirements and industry standards through a proactive approach to risk management.
The benefits of cyber risk assessment services include:
- Enhanced security posture: Proactively reinforces protections against cyber threats.
- Compliance: Facilitates adherence to regulatory and industry standards.
- Reduced financial loss: Minimizes exposure to the risks of data breaches and operational disruptions.
- Improved decision-making: Delivers actionable insights to support informed security strategies.
- Strategic planning: Establishes a framework for advancing organizational cybersecurity initiatives.
Cyber risk assessment services can encompass:
- Vulnerability detection: Specialists assess your IT environment to identify weaknesses in systems, applications, and networks.
- Threat analysis: Identifies potential cyber threats—such as ransomware, phishing, and insider risks—that may exploit identified vulnerabilities are recognized.
- Risk evaluation: The likelihood of threats being exploited and their potential impact on business operations and data is measured.
- Action plans: A prioritized list of recommended actions is developed based on the risk evaluation, following frameworks like NIST.
- Reporting and guidance: A comprehensive report on security posture is provided with practical recommendations for implementing necessary controls and best practices.
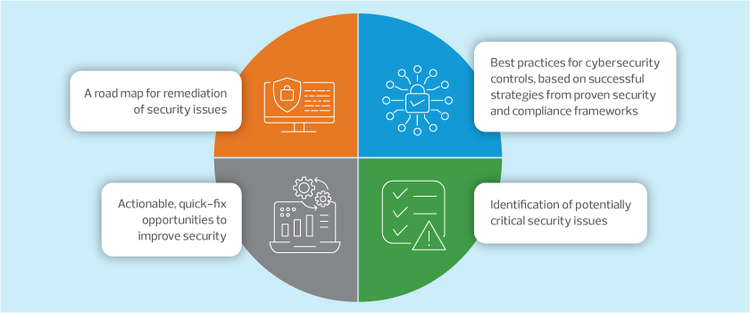
RSM’s customized cyber risk assessment determines your risk exposure, includes advice on potential process gaps and realistic action plans, and provides you with a high-level view of your organization’s cybersecurity maturity. Key RSM deliverables include:
Who needs a cyber risk assessment?
According to the RSM US Middle Market Business Index Cybersecurity Special Report, nearly 68% of executives surveyed expect that unauthorized users will attempt to breach their data or systems this year. A cyber risk assessment can help your organization gain a better understanding of your security program and communicate program maturity to key stakeholders, clients and vendors. Since the cyber risk assessment covers a wide range of security controls, your organization can pinpoint areas of strength and weakness, plan accordingly and mark progress over time.
How can a cyber risk assessment help protect your business?
A cyber risk assessment is particularly beneficial to establish baselines for your current security program, benchmark your maturity against peers and identify critical points of weakness. It also reveals whether gaps stem from weaknesses in personnel, processes or technology. This helps your organization prioritize areas of remediation and allocate resources where they are most needed.
Cyber risk assessment services
Cyber risk assessment services are consulting engagements provided by third-party advisors who analyze an organization's IT systems, policies, and security controls to identify vulnerabilities, assess potential threats and their impacts, and prioritize remediation steps to improve security posture and achieve compliance.
RSM’s cyber risk assessment services include an information security assessment and our cyberthreat intelligence services, all tailored to the unique needs of your industry and your specific security concerns.
- NIST Cybersecurity Framework assessment: This assessment, based on the framework established by the National Institute of Standards and Technology, is an interview-based review of your security controls. The effectiveness of each control is determined by evaluating its policies, procedures and formal governance as well as its technical implementation. Assessment of all your controls provides insight into the maturity of your security program.
- Cyberthreat intelligence services: Nearly all the data stolen from companies is located in the deep web and the dark web, areas difficult to access and navigate without a high level of knowledge and experience. We investigate these areas and common threat actor communication platforms to determine if attackers are currently targeting your organization or industry.
Related cybersecurity services
In addition to the services offered through our cyber risk assessment, we provide the following add-on services for clients who want a deeper look at certain aspects of their security program:
- Strategic and operational planning: Through this process, our team uncovers areas that require better protections for critical data and systems, and provides valuable data analytics and planning to align your security program with your company mission. Use this service to strengthen security and risk management initiatives and incorporate them into current and future budgets, while also analyzing security spending, evaluating the effectiveness of your security projects, and determining whether security personnel are properly utilized.
- Incident response tabletop: These sessions are discussion-based simulations that apply incident response plans (IRPs) to realistic scenarios. The goal of these exercises is to gain a better understanding of the incident response documentation currently in place, including procedures for notification, escalation and containment, and to evaluate how your staff would respond to a security incident. This service includes review of lessons learned from simulations. Having a tested IRP, as well as personnel familiar with the policies and procedures associated with this plan, can reduce the impact of security events.
- Firewall assessment: Firewalls are often the first line of defense for a network, but often exhibit significant weaknesses, making attacks that much easier. A firewall assessment analyzes your configuration line by line and ensures it meets best practices and utilizes effective hardening techniques.
Additional cybersecurity solutions
- /services/risk-fraud-cybersecurity/cybersecurity-business-vulnerability/cyber-resiliency
- /services/risk-fraud-cybersecurity/cybersecurity-business-vulnerability/secure-architecture
- /services/risk-fraud-cybersecurity/cybersecurity-business-vulnerability/cybersecurity-risk-compliance
- /services/risk-fraud-cybersecurity/cybersecurity-business-vulnerability