Cybersecurity challenges for financial services organizations
Key takeaways
Financial services organizations continue to be among the industries most targeted for cyberattacks. Banks, lenders, investment firms and payment processors sit at the intersection of sensitive data, global money movement and critical infrastructure, making them attractive targets for cybercriminals, hacktivists and nation‑state actors alike.
The cybersecurity risk profile for the financial services industry is driven by the type of data financial firms hold, the role that data plays in the broader economy and the monetary value of that data. Attackers can quickly monetize personally identifiable information, account credentials and direct access to funds. Beyond that, many financial institutions serve as clearinghouses or processors for others, meaning a single disruption can ripple far across the financial ecosystem.
Addressing cyber vulnerabilities is much more than a risk issue; it’s also a competitive imperative, given that 81% of middle market organizations across all industries plan to increase their cybersecurity budget this year, according to the RSM US Middle Market Business Index Special Report: Cybersecurity 2026.
To strengthen operations overall, financial services organizations should embed cybersecurity resilience into their enterprise risk management framework. This requires a holistic, top-down approach to security, led by the board of directors and executive leadership.
Here are three of the most prominent factors that shape the cybersecurity landscape for financial services organizations:
1. The rise of third-party and fintech relationships
Data is increasingly shared across vendors, platforms and cloud environments, expanding the attack surface and complicating oversight. Artificial intelligence, increasingly embedded into fintech platforms, adds another dimension of risk when it comes to data loss.
“Even just 10 years ago in financial services, there was nowhere near the vendor and partnership connectivity there is now,” says Joe Strain, an RSM US LLP director who focuses on cybersecurity risk and data protection. “Traditional, risk-averse banks are now very integrated with multiple cloud platforms, several software as a service (SaaS) solutions, and fintech; the data sprawl is immense.”
As organizations modernize their technology stacks, security controls must keep pace.
2. Regulation does not always guarantee security
The financial services industry is among the most heavily regulated, and compliance remains a significant operational burden. But regulatory compliance alone does not guarantee cybersecurity resilience.
Policies and controls may exist on paper but fail to materially reduce real‑world threats. This disconnect can create a false sense of confidence. While compliance establishes a baseline, it does not prescribe how to design secure systems or respond to emerging attack techniques such as deepfake‑enabled fraud or ransomware threats.
3. Social engineering and ransomware continue to evolve
Attackers are increasingly using AI to craft sophisticated social engineering campaigns. These attacks mimic executive communication styles and often target employees involved in wire transfers and payment approvals.
Ransomware has also evolved. Even organizations with strong backups may face pressure from “double extortion” tactics, where attackers threaten to publish sensitive data if a ransom is not paid. For financial institutions built on trust and reputation, this risk can be especially damaging.
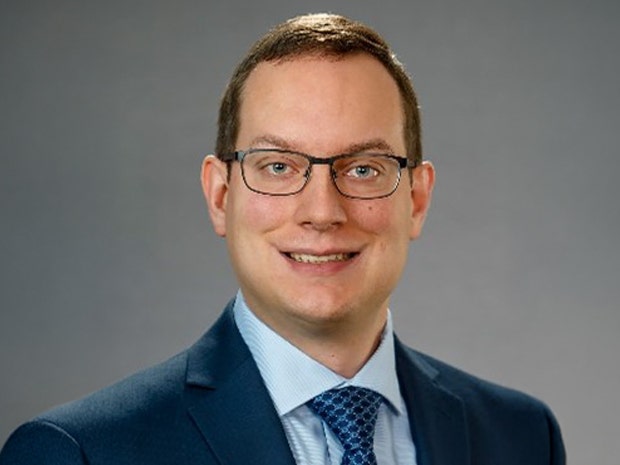
“Cybersecurity is everybody's problem. This does not just fall to the cyber team; everyone in the organization has a very big part to play.”
Joe Strain, Director, RSM US LLP
How can financial services organizations respond?
Cybersecurity cannot be isolated within the IT or security function. From finance and operations to executive leadership, employees across the organization influence cyber risk exposure through daily decisions, access privileges and response behaviors; all teams need to take responsibility for understanding and addressing the risk.
“Cybersecurity is everybody's problem,” says Strain. “This does not just fall to the cyber team; everyone in the organization has a very big part to play.”
To address the current cyberthreat landscape, organizations should consider the following priorities:
Financial services organizations need to be proactive in addressing the current threat landscape. Working with a third-party advisor on the actions above can help institutions manage risk and boost their cybersecurity resilience.
Related insights
- /insights/services/risk-fraud-cybersecurity/resiliency-planning-key-for-financial-institutions
- /insights/industries/financial-services/cybersecurity-risk-mitigation-bank-ecosystems
- /insights/industries/financial-services/key-considerations-for-financial-institutions-core-system-strate